
Everything you need to stop reacting and start deciding.
Built by a defender who lived the pain of manual CVE triage. Import from any scanner, enrich with real exploit intelligence, map to compliance, and act — all in one workflow.
Works with the scanners you already run
Product Tour
A real platform — captured from the demo workspace
Screenshots from the sample demo workspace (captured April 2026, before the interface redesign). Every view is interactive at cveriskpilot.com/demo.
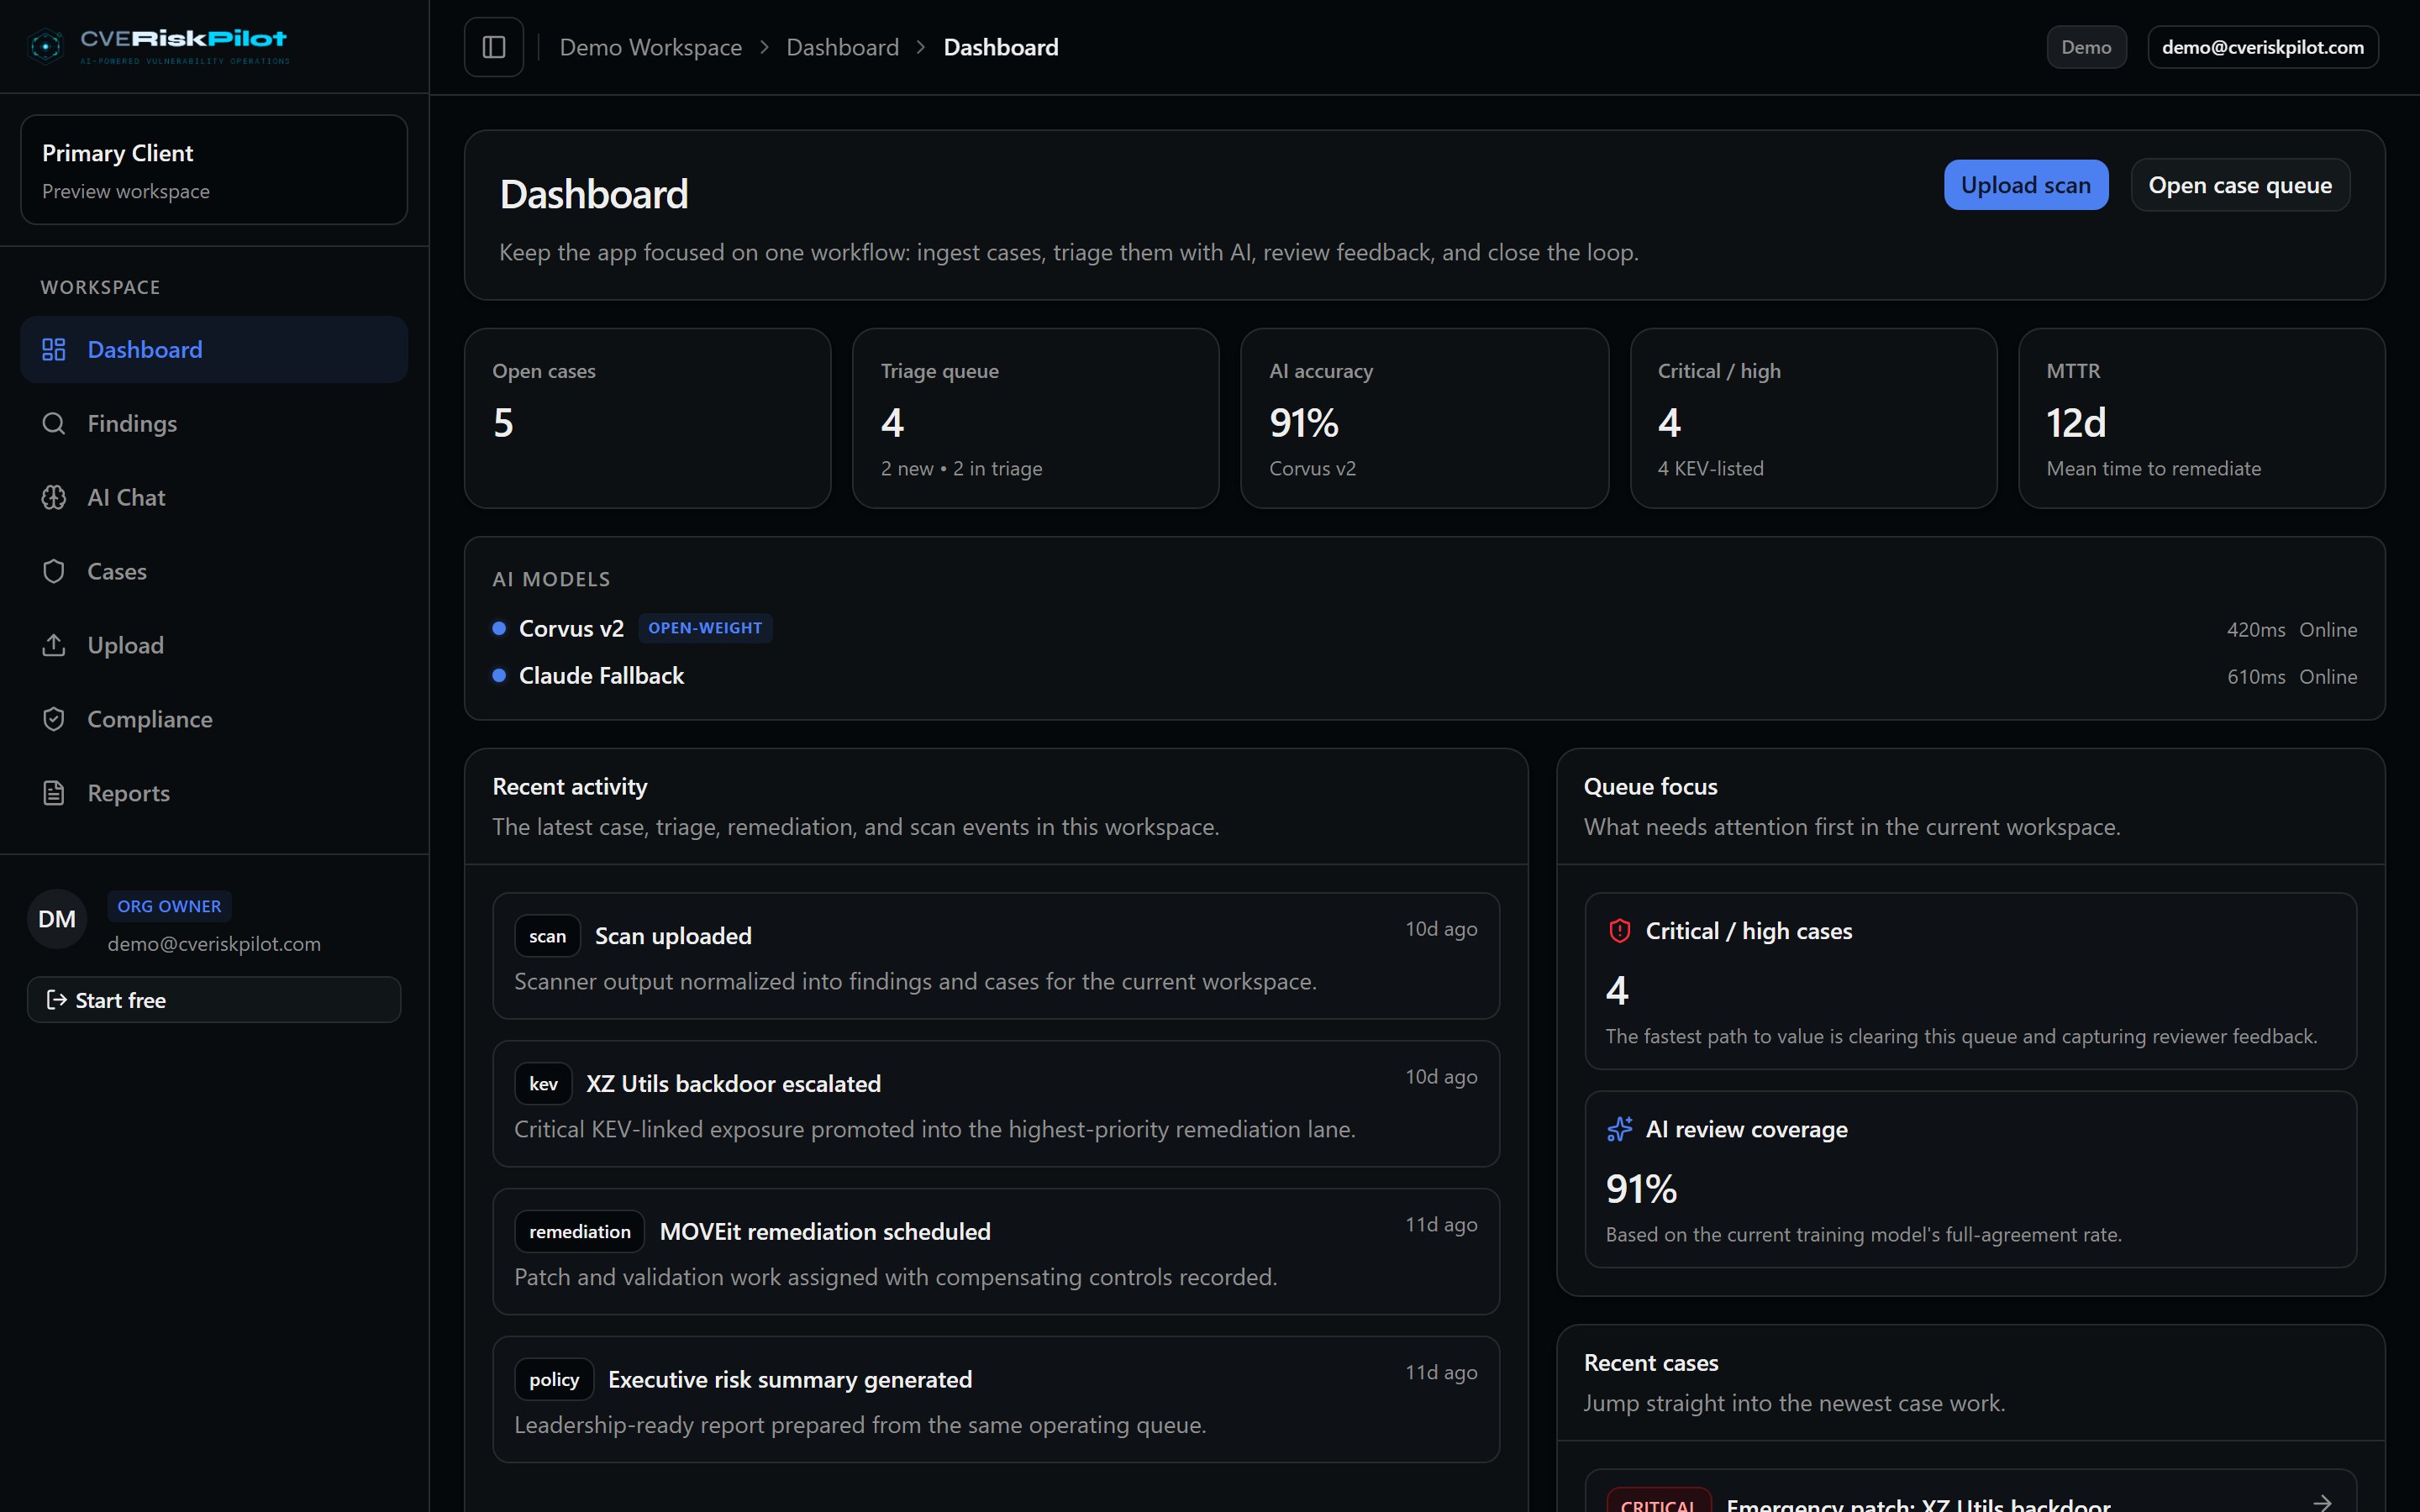
Executive dashboard
Real-time posture — open findings, KEV exposure, SLA compliance, severity breakdown.
Open demo view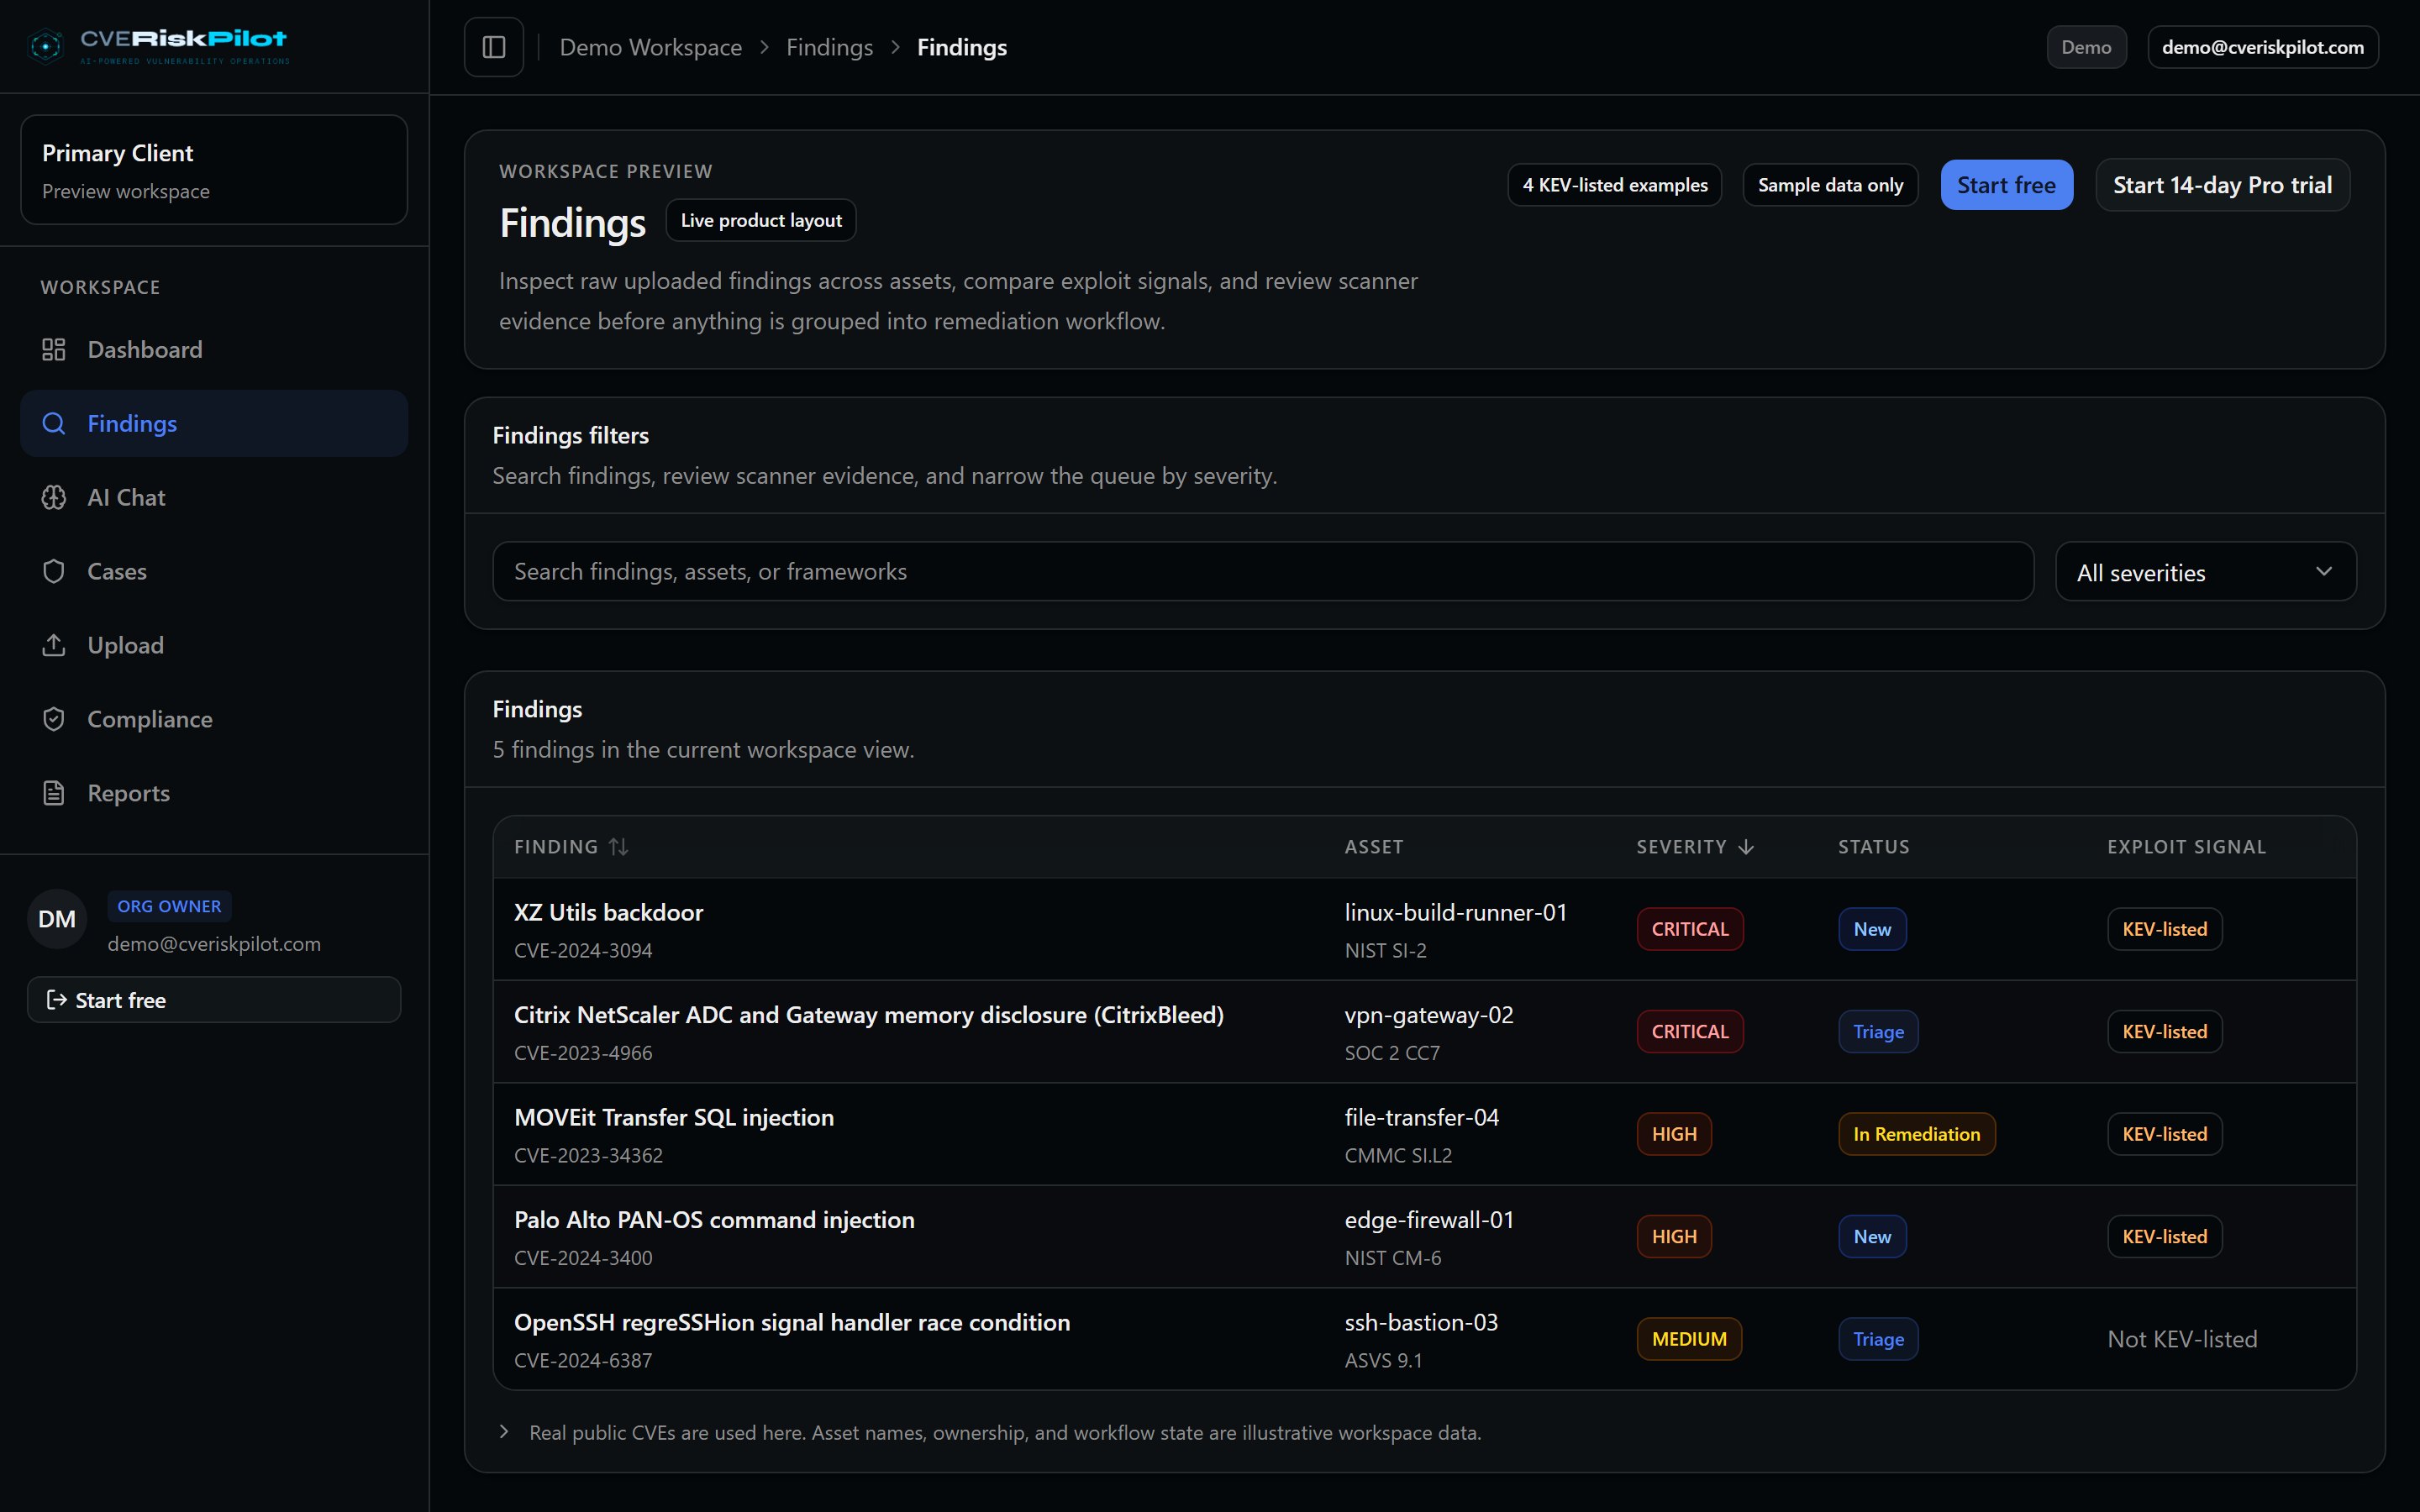
CVE triage queue
Each finding enriched with EPSS, CISA KEV, CWE, asset context, and compliance mapping.
Open demo view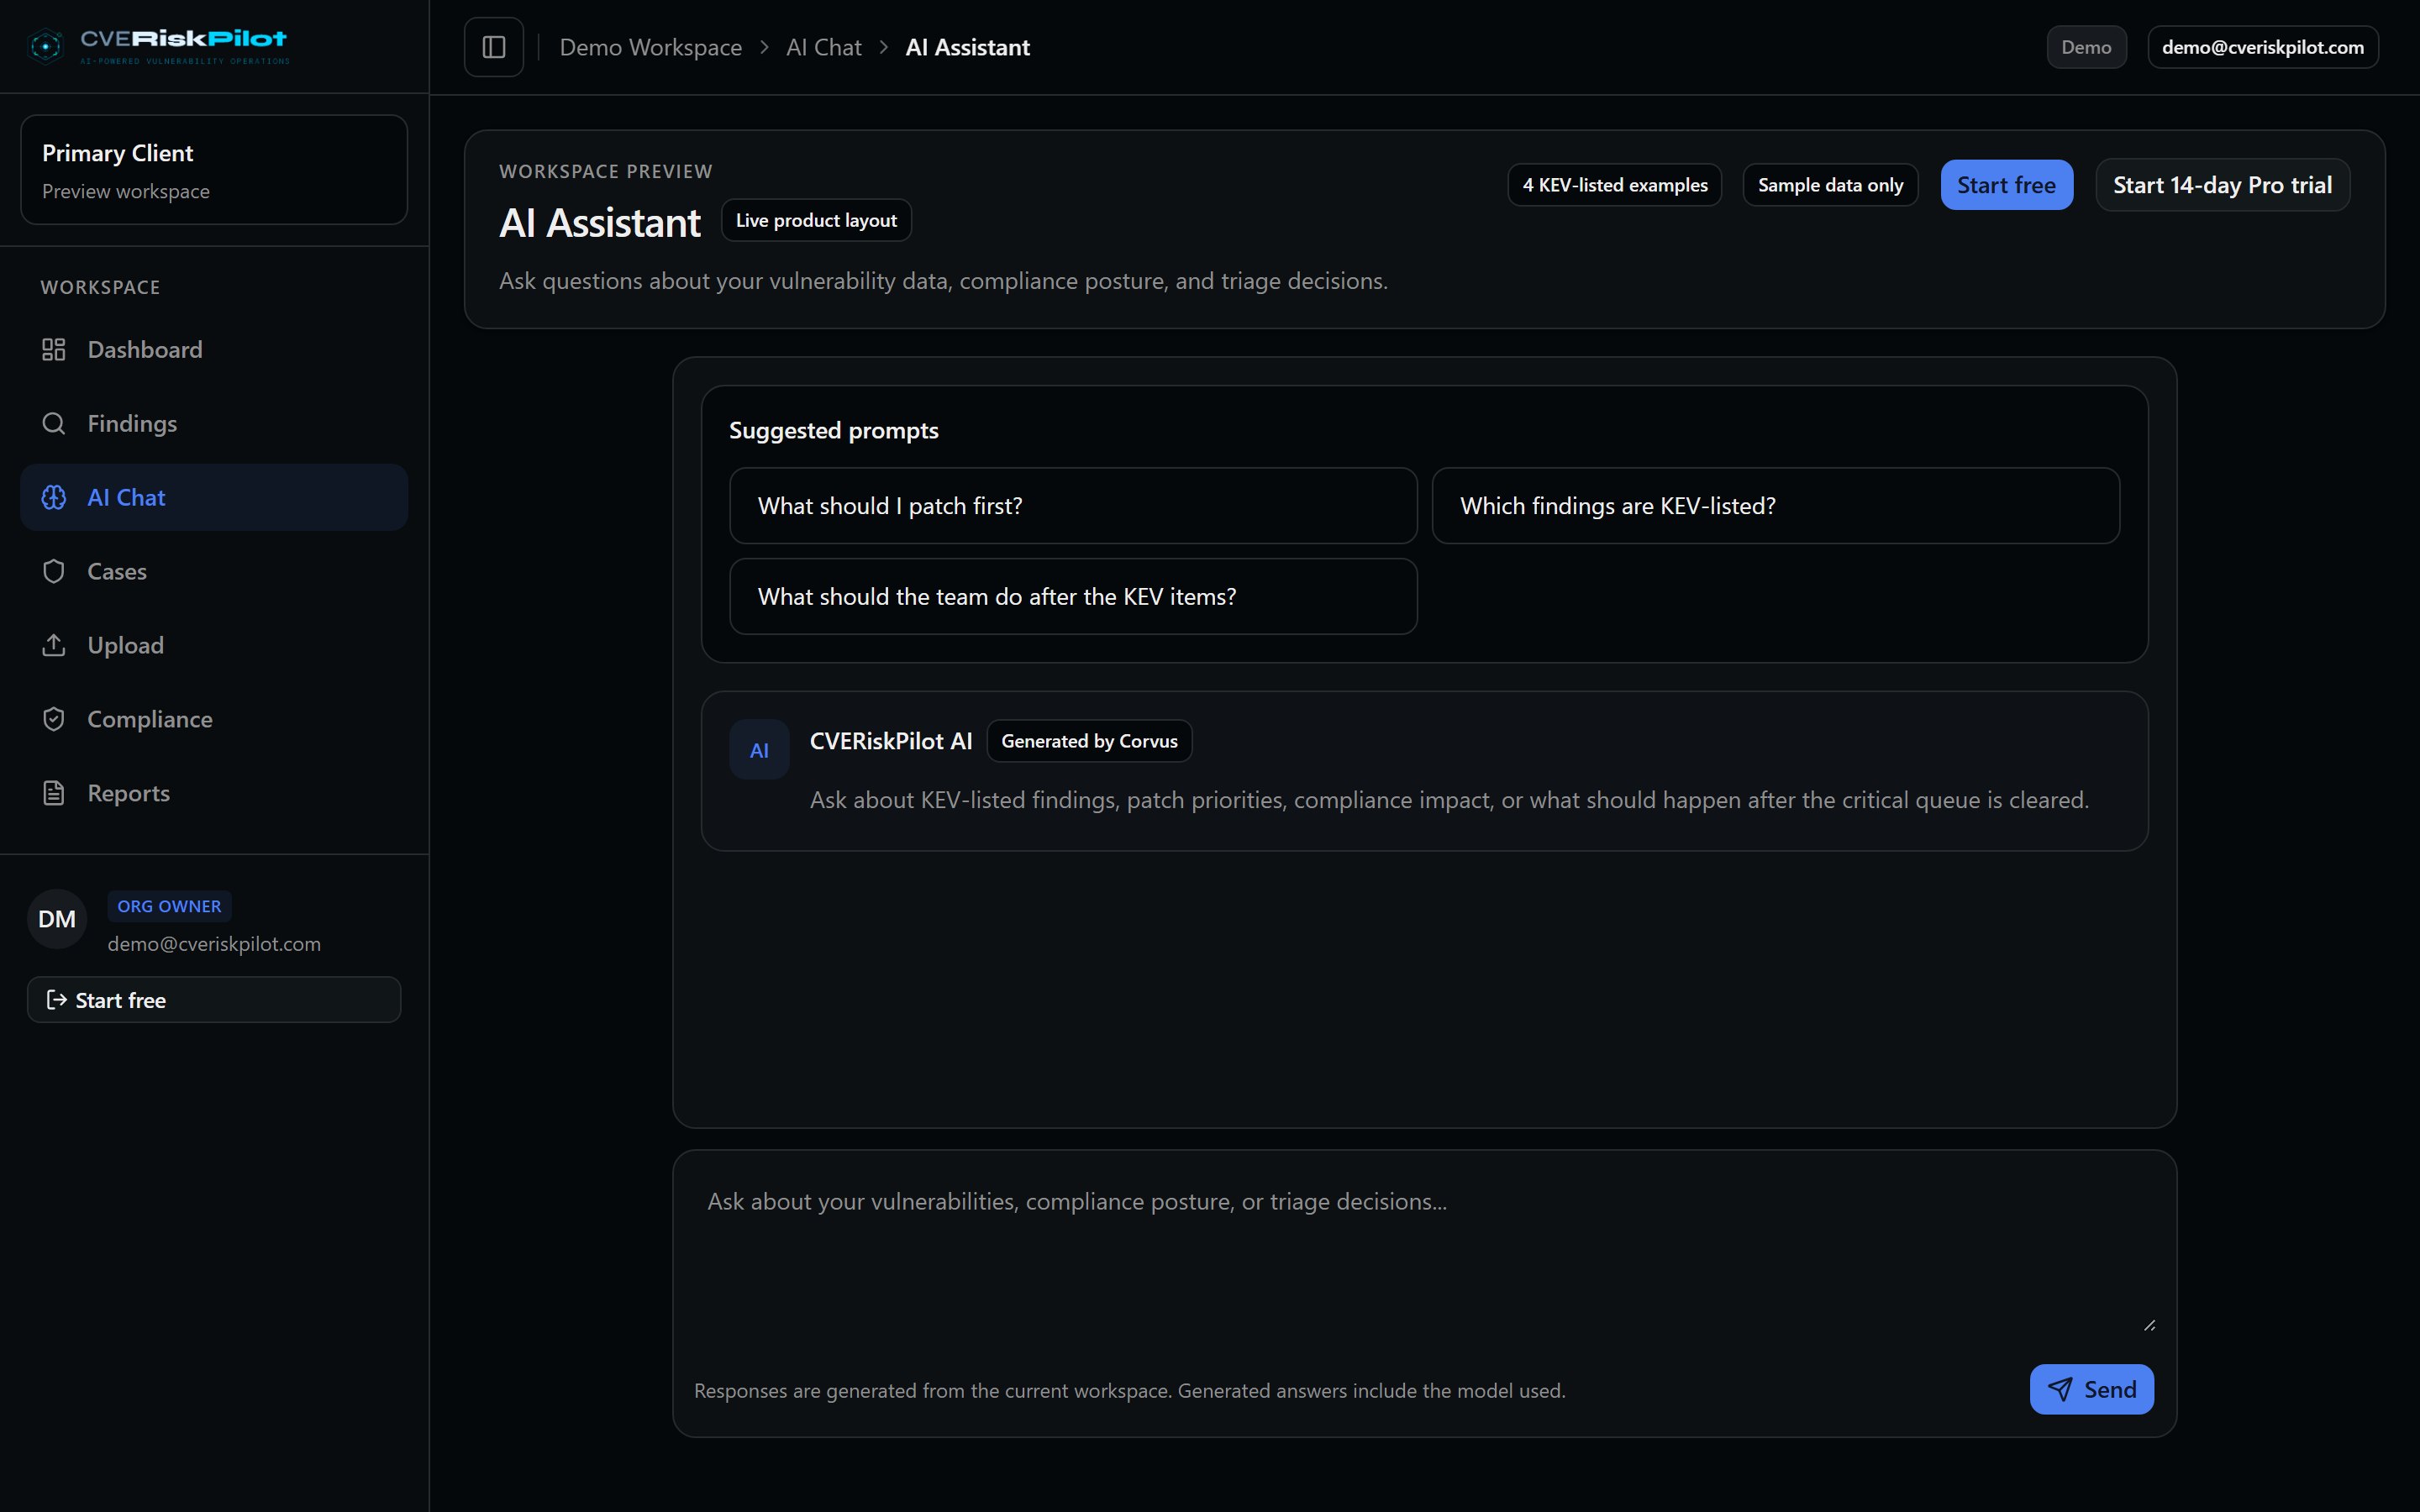
AI triage assistant
Ask natural-language questions about your own findings, cases and compliance posture, answered by an external AI model with refusal and spend guards.
Open demo view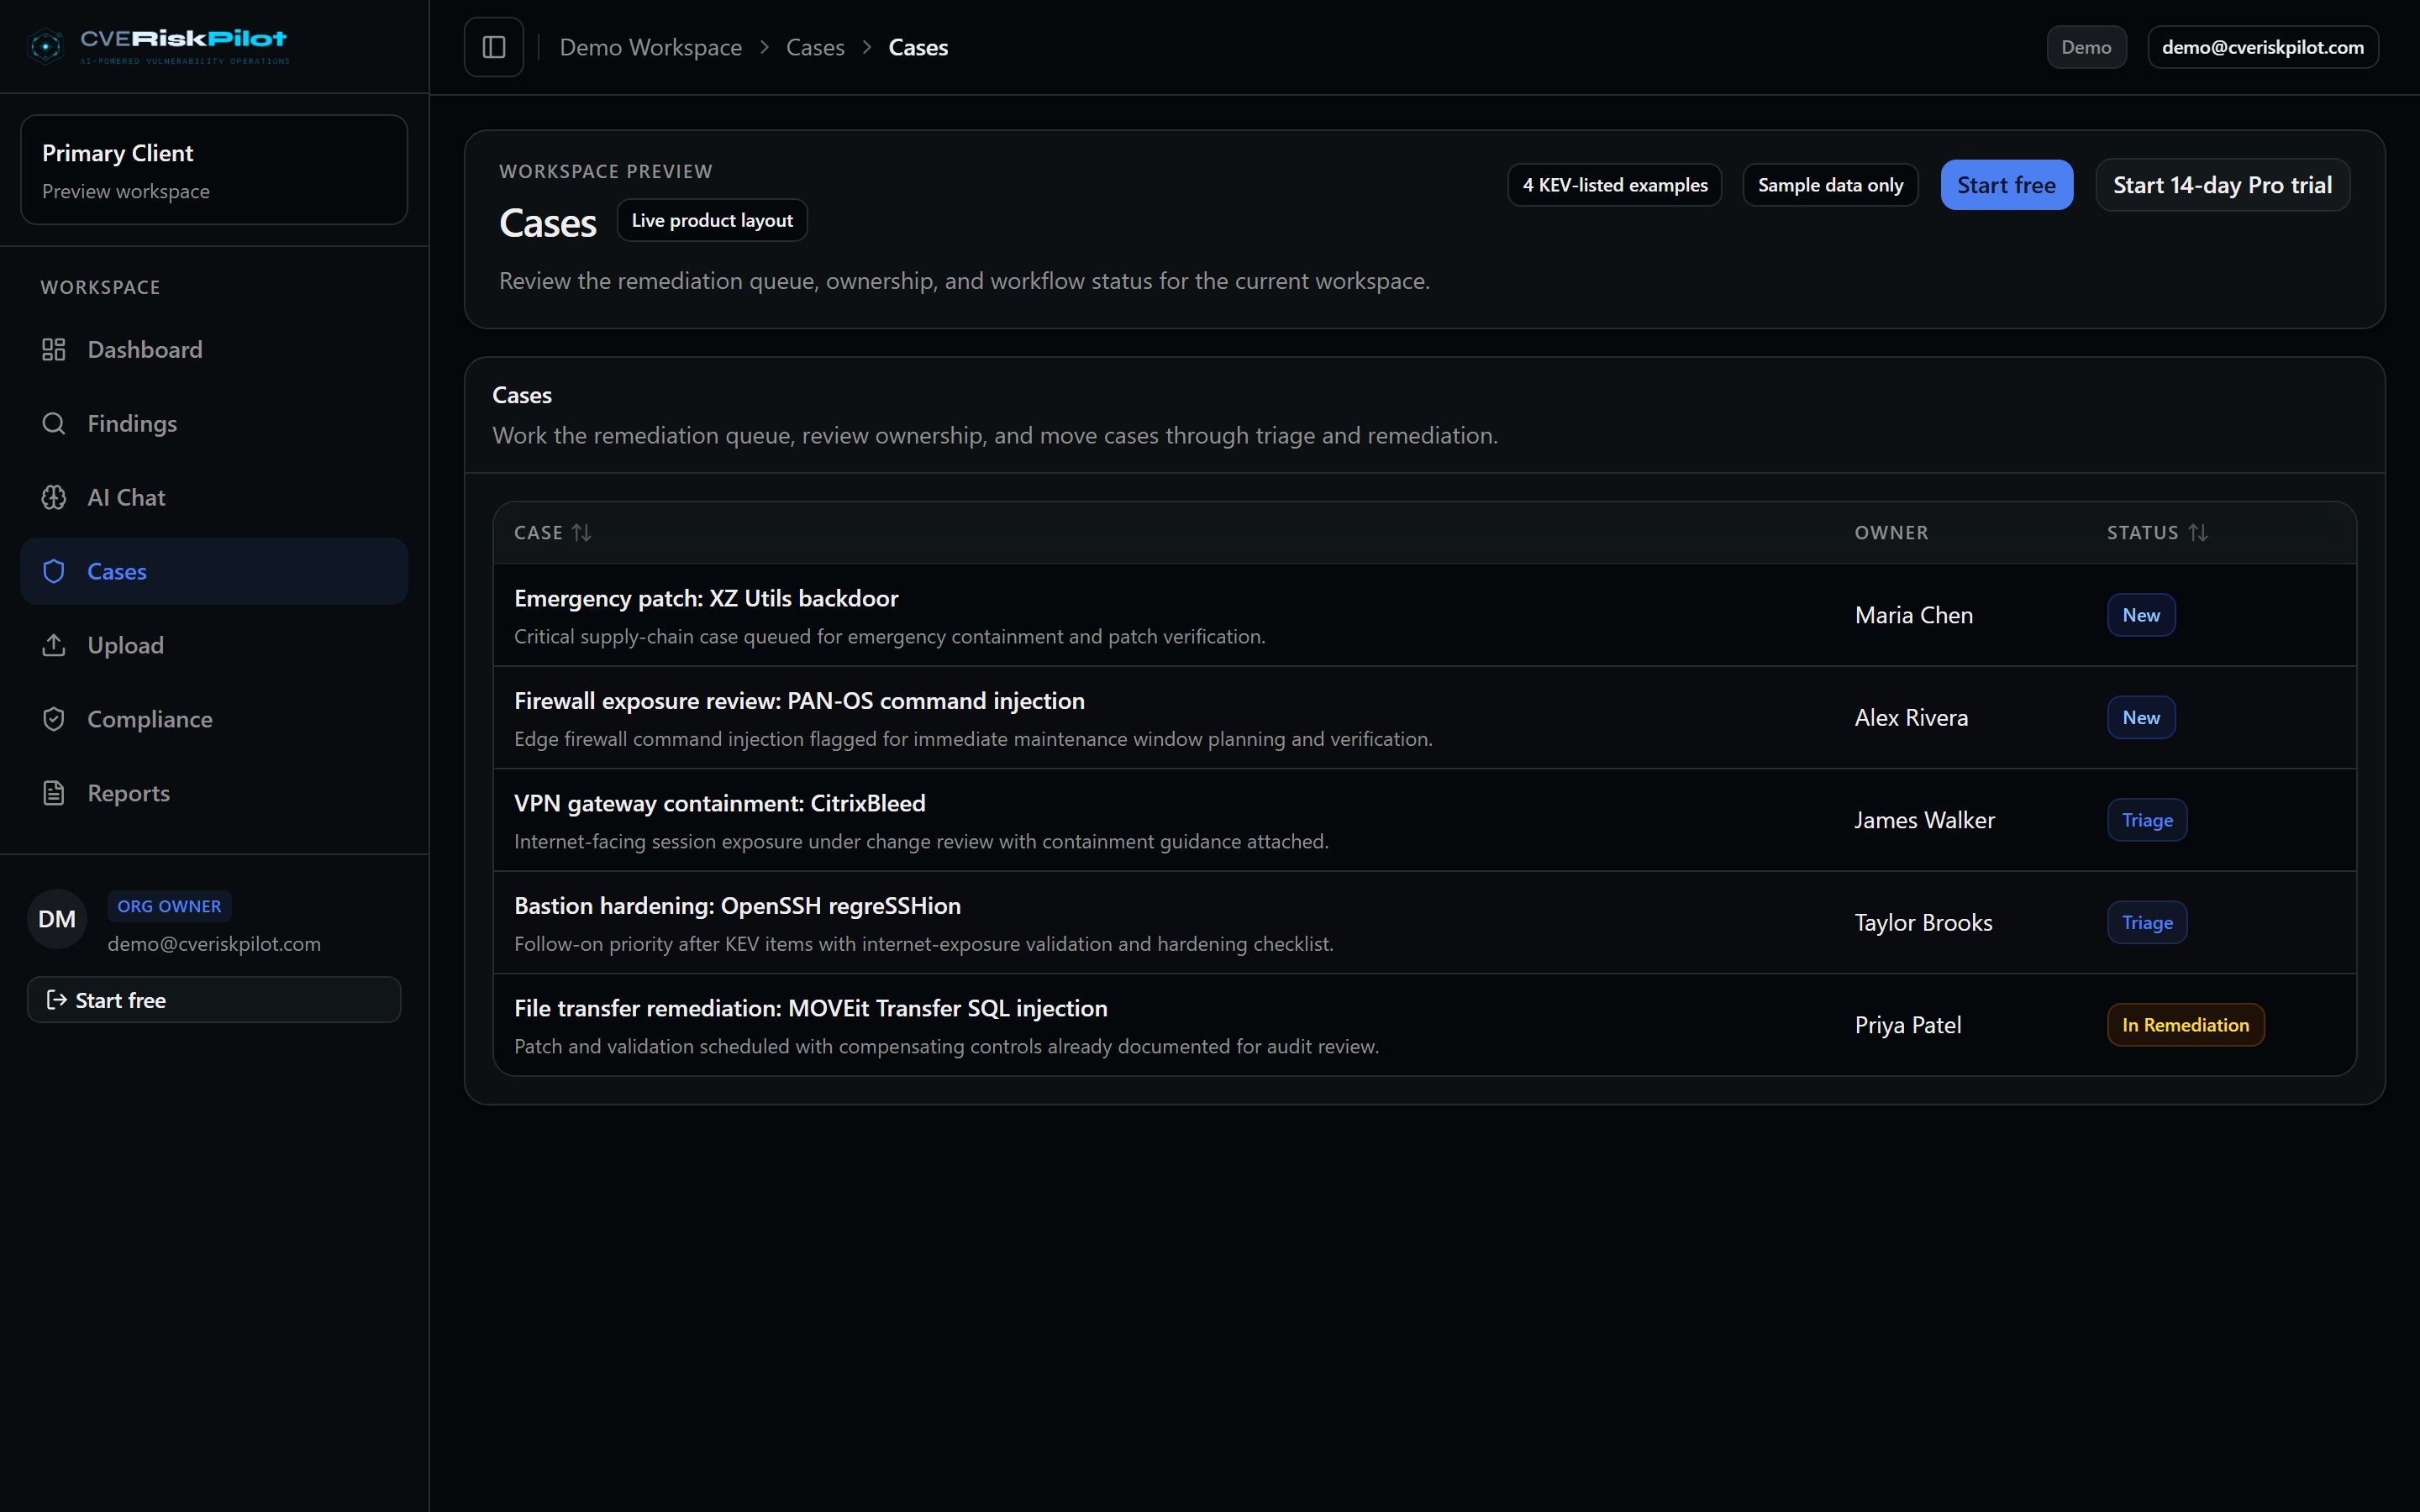
Case management
Risk acceptance, compensating controls, false-positive justification — audit-trailed.
Open demo view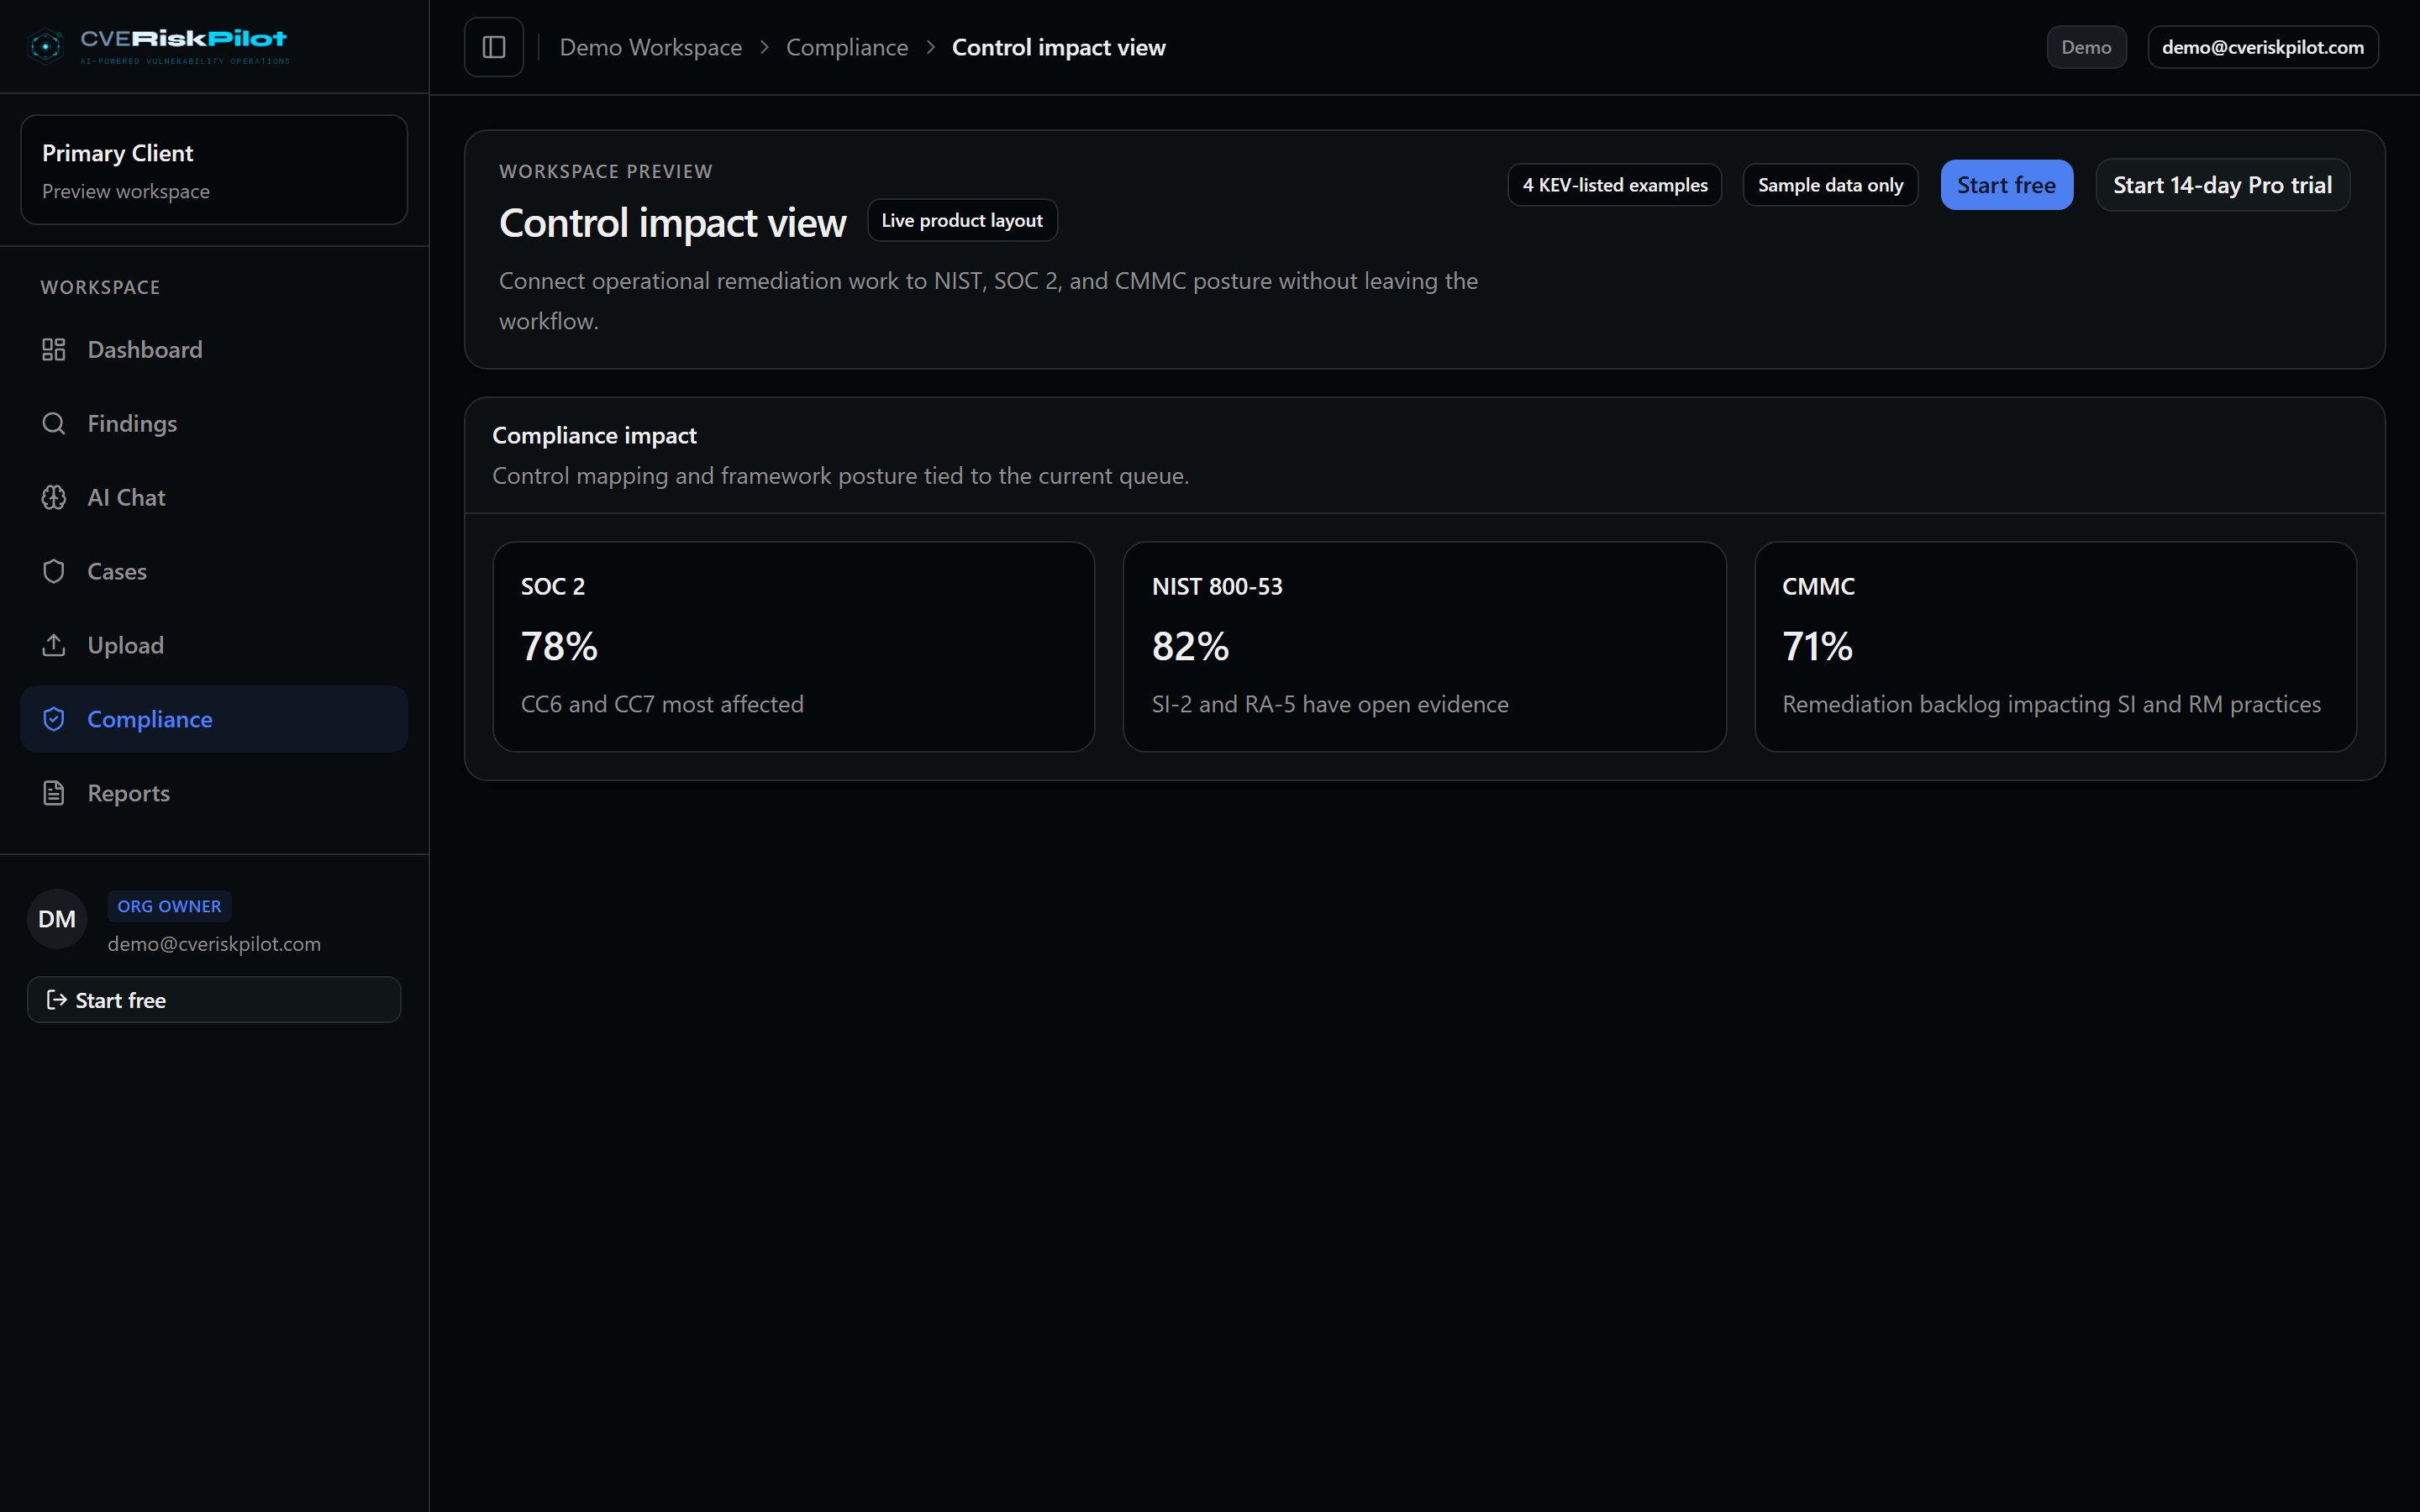
Compliance mapping
CWE-to-control bridge across 13 frameworks: NIST 800-53, SOC 2, CMMC, FedRAMP, HIPAA, PCI, ISO 27001 +.
Open demo view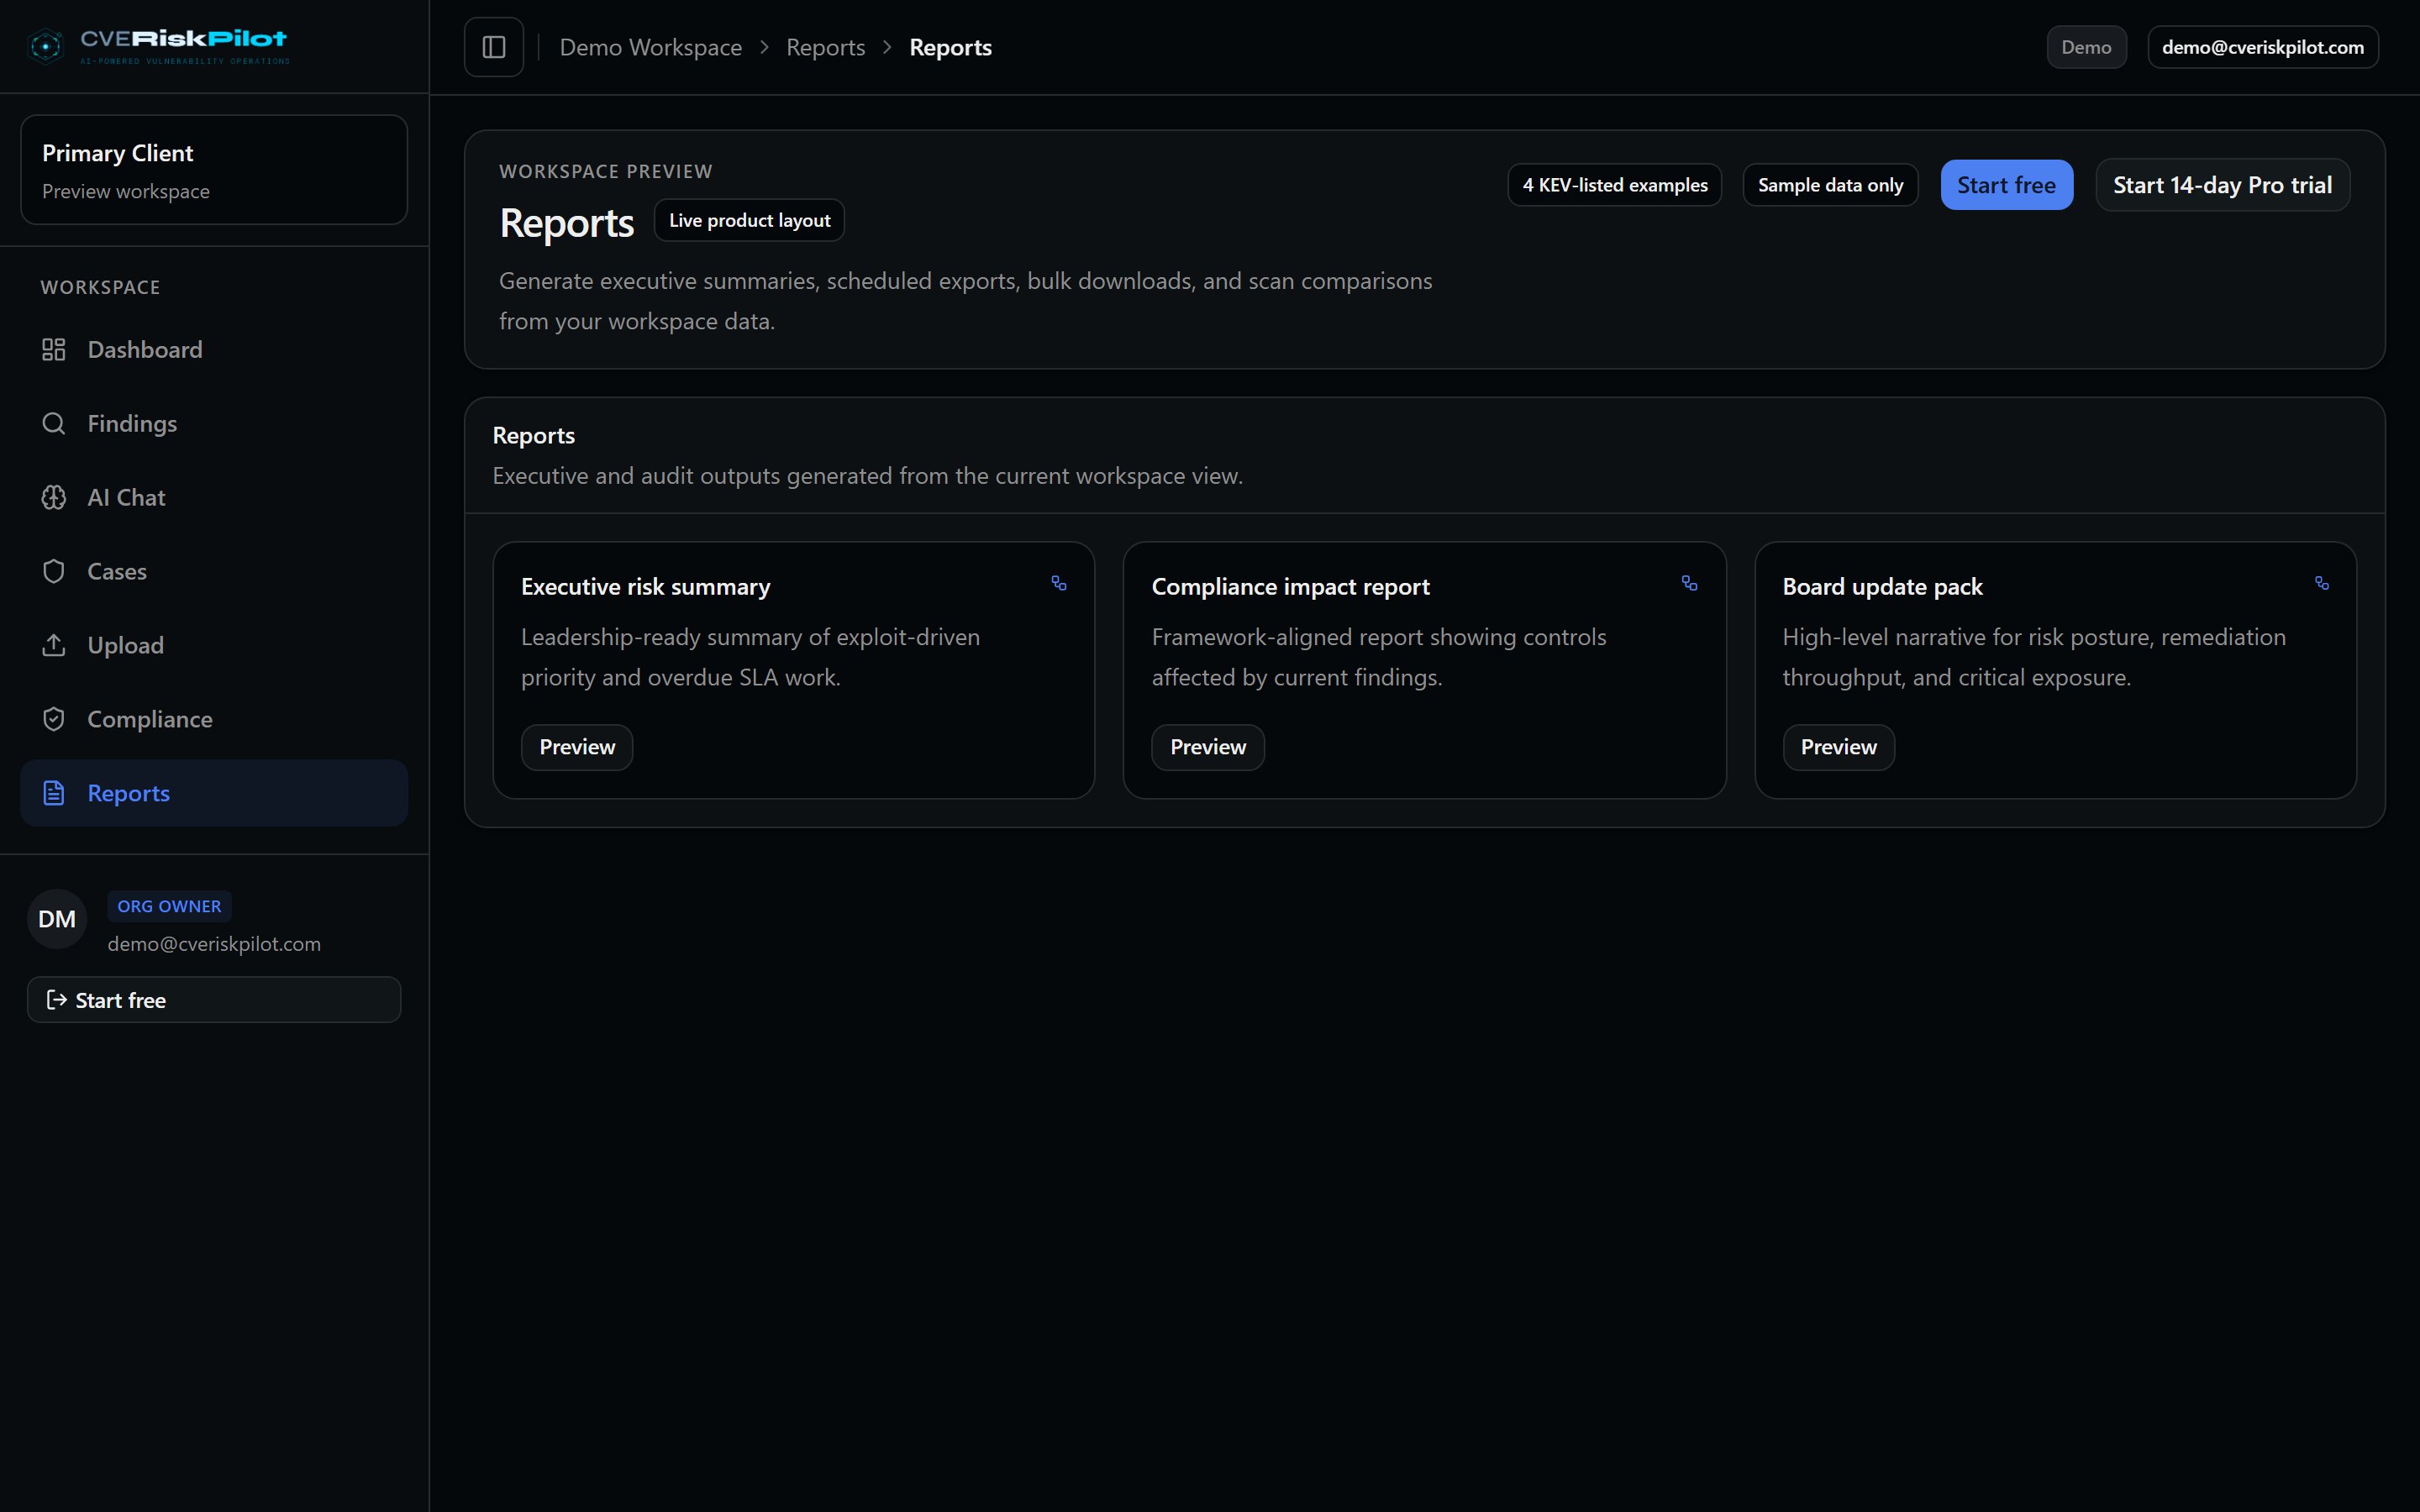
Audit-ready reports
POAM generation, evidence bundles, and a hash-chained audit log (Ed25519 signing in progress).
Open demo viewThe demo workspace runs on sample data with pre-written AI replies. The product interface has been redesigned since these images were captured.
Ingestion Layer
One platform. Every scanner you already use.
Don't replace your existing tools. CVERiskPilot sits on top of them, ingesting output from every major scanner in their native format and normalizing everything into one decision-ready model.
- 11 scanner format parsers (Nessus, SARIF, CycloneDX, Qualys, OpenVAS, SPDX, OSV, CSAF, CSV, JSON, XLSX)
- Scanner API connectors for Tenable, Qualys, CrowdStrike, Rapid7 and Snyk (in progress; export and upload today)
- CLI scanner with 13 package manager formats
- Real-time push ingestion (Signal Engine, planned)
- SBOM import and correlation
Intelligence Layer
Stop treating every CVSS 9.8 the same.
Traditional tools dump a list sorted by CVSS. CVERiskPilot correlates each finding against exploit availability, CISA KEV status, EPSS probability, your asset criticality, and business context to produce a true risk score.
- NVD enrichment with CVSS vector parsing
- EPSS exploit probability scoring
- CISA KEV correlation at ingest and enrichment
- Asset criticality weighting
- AI-generated risk narratives and business impact statements
- Cortex Analytics for natural language compliance queries
AI Decision Layer
Guarded AI decisions, with a private-runtime path.
Production AI runs through explicit request paths with human review; Claude and NVIDIA NIM calls sit behind a daily spend guard, and triage and remediation prompts are redacted. Corvus is the private-runtime path for routine triage once serving and benchmark gates are healthy.
- Corvus private-runtime roadmap — buyer-facing claims gated by benchmark evidence
- Training data pipeline uses validated sources and reviewed human feedback exports
- Risk-based AI routing across external models, with a private Corvus path in progress
- Human-in-the-loop feedback flywheel
- Risk acceptance workflows with approval gates
- POAM generation with CSV, JSON and XLSX export
- "Not exploitable because..." drafts (Auditor Agent, in internal testing)
Compliance Mapping
Findings mapped across 13 frameworks.
CVERiskPilot maps each finding that carries a CWE to the compliance controls it threatens, across up to 13 frameworks. See your compliance posture score per framework and generate audit-ready evidence packages.
- NIST 800-53, CMMC, SOC 2, FedRAMP
- HIPAA, PCI DSS, ISO 27001, NIST CSF 2.0
- GDPR, ASVS, SSDF, EU CRA, NIS2
- CWE-to-control bridge for automated mapping
- Per-framework compliance posture scores
- Cross-framework impact analysis
Trust Layer
A tamper-evident record of your decisions.
Security-relevant actions are recorded in a per-organization hash-chained audit log, so editing or removing an entry breaks the chain. Ed25519 signatures and Merkle inclusion proofs (Vault Protocol) are in progress.
- Ed25519 signing of audit entries (in progress)
- Merkle inclusion proofs (in progress)
- Tamper-evident audit log with hash chaining
- Evidence collection for SOC 2 / CMMC / FedRAMP audits
- Signed audit export an auditor can verify (in progress)
Action Layer
Push to the workflows your team already runs.
Move from triage to ticket without manual reformatting. Push cases to Jira and ServiceNow and assign them singly or in bulk; automation rules that route and assign findings (Flux Pipelines) are planned.
- Jira and ServiceNow integration
- Automation rules for routing and assignment (Flux Pipelines, planned)
- Scheduled CVE intelligence digests
- Executive reports and evidence packages
- Signed test webhook delivery (event delivery planned)
- CSV export for findings and cases; executive summary and case reports as PDF
Compliance impact, per finding
Scanners tell you a CVE is critical. Compliance platforms tell you a framework is partially complete. CVERiskPilot connects the two: every finding with a mapped CWE shows which controls it threatens, and every remediation is tied to the control gaps it helps close.
- Scanners:
- “CVE-2023-34362, CVSS 9.8, in MOVEit Transfer.”
- GRC platforms:
- “SOC 2 — 78% complete.”
- CVERiskPilot:
- “Its CWE (CWE-89) maps to 18 controls across 10 frameworks, including SOC 2 CC6.8.”
Finding detail
18 controls affectedSQL injection in MOVEit Transfer
Remediation impact: Fixing this CVE helps close gaps in 18 mapped controls across 10 frameworks.
See these features in action
Try the live demo with realistic data, or start free with your own scans. No credit card required.